Security and trust
This page lists controls that exist in the product today, with where they come from. Planned capabilities are marked as planned; no certification or compliance approval is claimed.
Role-based access
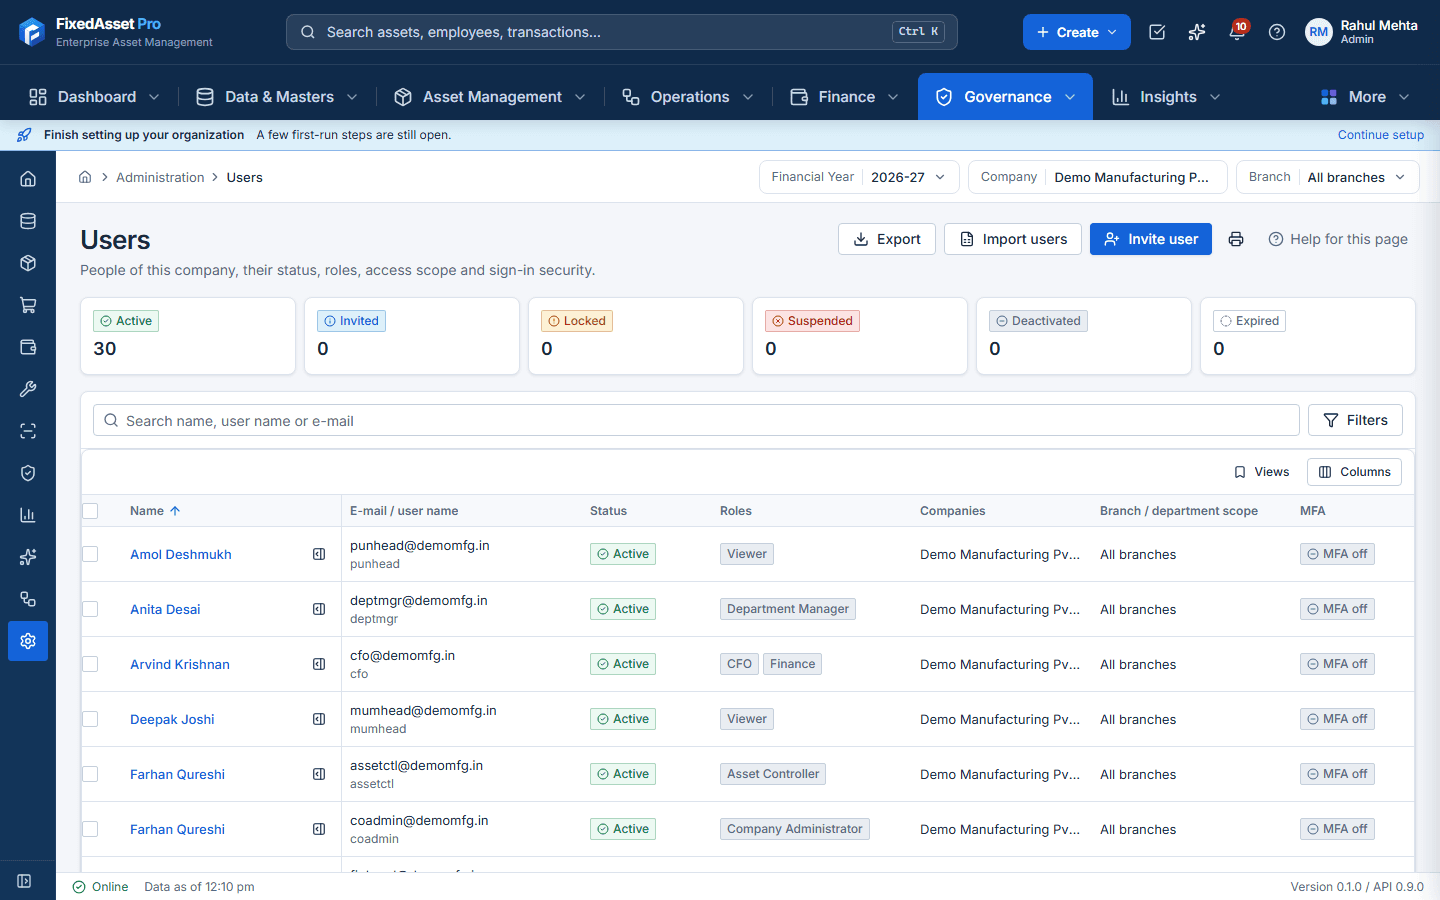
Ten built-in roles from Administrator to Verifier plus custom roles with granular permissions; amounts are hidden from users without finance rights.
Company and branch scoping
Users see only the companies, branches and locations they are given; each organisation's data is isolated.
Audit logging
Who, when, old value, new value and reason for every change. The log is sealed every 15 minutes into a hash chain, verified daily, anchored to a file, cannot be switched off, and lists out-of-band database changes separately.
Secure authentication
Password policy and lockout, multi-factor authentication (authenticator app, recovery codes, e-mail one-time code), LDAP / Active Directory and OpenID Connect single sign-on. Codes and secrets are never logged.
Session management
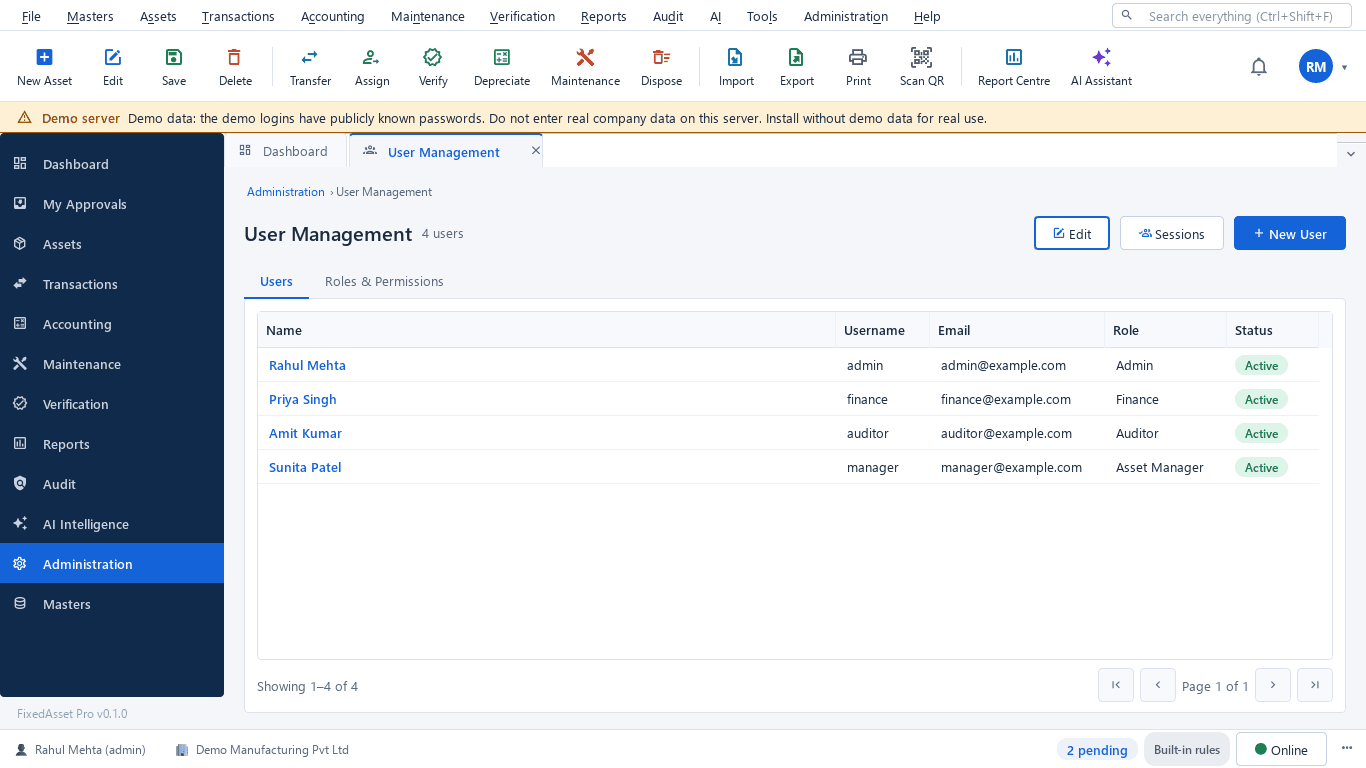
Sessions can be listed and ended; remembered devices expire by policy; service users hold scoped API keys with expiry, IP allow-lists, rate limits and rotation.
Protected documents
Versioned documents in the evidence vault; evidence packs carry a SHA-256 checksum, cannot be deleted and can be re-checked for integrity on demand.
Backup and recovery
Scheduled backups in AES-256-GCM encrypted archives opened only with your passphrase, off-machine targets, restore tests and point-in-time recovery; a guarded restore can be rolled back within 7 days.
Configurable hosting
Cloud-hosted web edition, or the desktop edition on your own Windows server where no internet is needed for daily work.
Transport security on the LAN
LAN clients pin the server's certificate fingerprint: only that exact certificate validates, and a changed certificate must be re-pinned by the user.
AI governance
AI reads only what the user may see, never changes records, and keeps a hash-chained activity log; cloud AI is off by default on the desktop edition.
Planned and not claimed
- Certifications (for example ISO 27001 or SOC 2) are not claimed; we will publish them only with the supporting evidence.
- A public service-status page and subprocessor list will be linked here when they exist.
- Hybrid operation between a LAN installation and the cloud service is not available.
Security questions or a responsible disclosure: write to support@globalsynapsetech.com. support@globalsynapsetech.com