
Data Processing Agreement
1. Parties and purpose
This Data Processing Agreement ("DPA") is entered into between the customer organisation that has accepted the FixedAsset Pro Terms of Service ("Customer") and Global Synapse Technologies ("Provider"). It forms part of the Terms of Service and applies automatically when the Customer uses the FixedAsset Pro cloud service.
This DPA sets out how the Provider processes personal data contained in Customer Data on the Customer's behalf, so that both parties meet their obligations under the Digital Personal Data Protection Act, 2023 and the rules made under it (together, the "DPDP Act") and, where applicable, the Information Technology Act, 2000 and the rules made under it.
2. Definitions
Terms defined in the Terms of Service have the same meaning here. In addition:
- Personal Data, Data Principal, Data Fiduciary, Data Processor, Processing and Personal Data Breach have the meanings given to them in the DPDP Act.
- Customer Personal Data means the Personal Data contained in Customer Data that the Provider processes on behalf of the Customer in the cloud service.
- Sub-processor means a third party engaged by the Provider that processes Customer Personal Data in order to provide the cloud service.
- Board means the Data Protection Board of India.
3. Roles of the parties
3.1 For Customer Personal Data, the Customer is the Data Fiduciary and the Provider is the Data Processor. The Customer determines the purposes and means of processing; the Provider processes Customer Personal Data only on the Customer's behalf and under this DPA.
3.2 For personal data that the Provider processes for its own purposes (for example account administration of the Customer's users, billing, website enquiries, security and legal compliance), the Provider is a Data Fiduciary, and its Privacy Policy applies instead of this DPA.
3.3 Desktop edition. This DPA does not apply to the FixedAsset Pro desktop edition. Data in the desktop edition is stored on computers owned or controlled by the Customer, and the Provider does not process it. If the Customer sends such data to the Provider (for example a file attached to a support request), the Provider will treat that data in accordance with sections 6 to 8 and 15 of this DPA.
4. Details of the processing
4.1 Subject matter. Hosting and operation of the FixedAsset Pro cloud service for fixed asset management, depreciation, verification, maintenance, procurement, audit and reporting.
4.2 Duration. The term of the Customer's subscription, plus the period after termination during which Customer Data remains available for export and is then deleted, as described in section 15.
4.3 Nature and purpose. Storage, organisation, retrieval, computation (such as depreciation runs and reports), display, transmission to the Customer's users, backup and restoration, support, security monitoring, and AI-assisted extraction and question answering when the Customer uses those features, in each case only to provide the cloud service to the Customer.
4.4 Categories of Data Principals. Depending on what the Customer enters, typically:
- the Customer's employees and other users of the service;
- employees and other individuals to whom assets are assigned as custodians;
- contact persons of the Customer's vendors, service providers, insurers, lessors and customers;
- auditors, consultants and other individuals named in records or documents;
- any other individuals whose data appears in documents uploaded by the Customer.
4.5 Categories of Personal Data. Depending on what the Customer enters, typically:
- identity and contact details: names, employee or vendor codes, designations, departments, e-mail addresses, phone numbers, office locations;
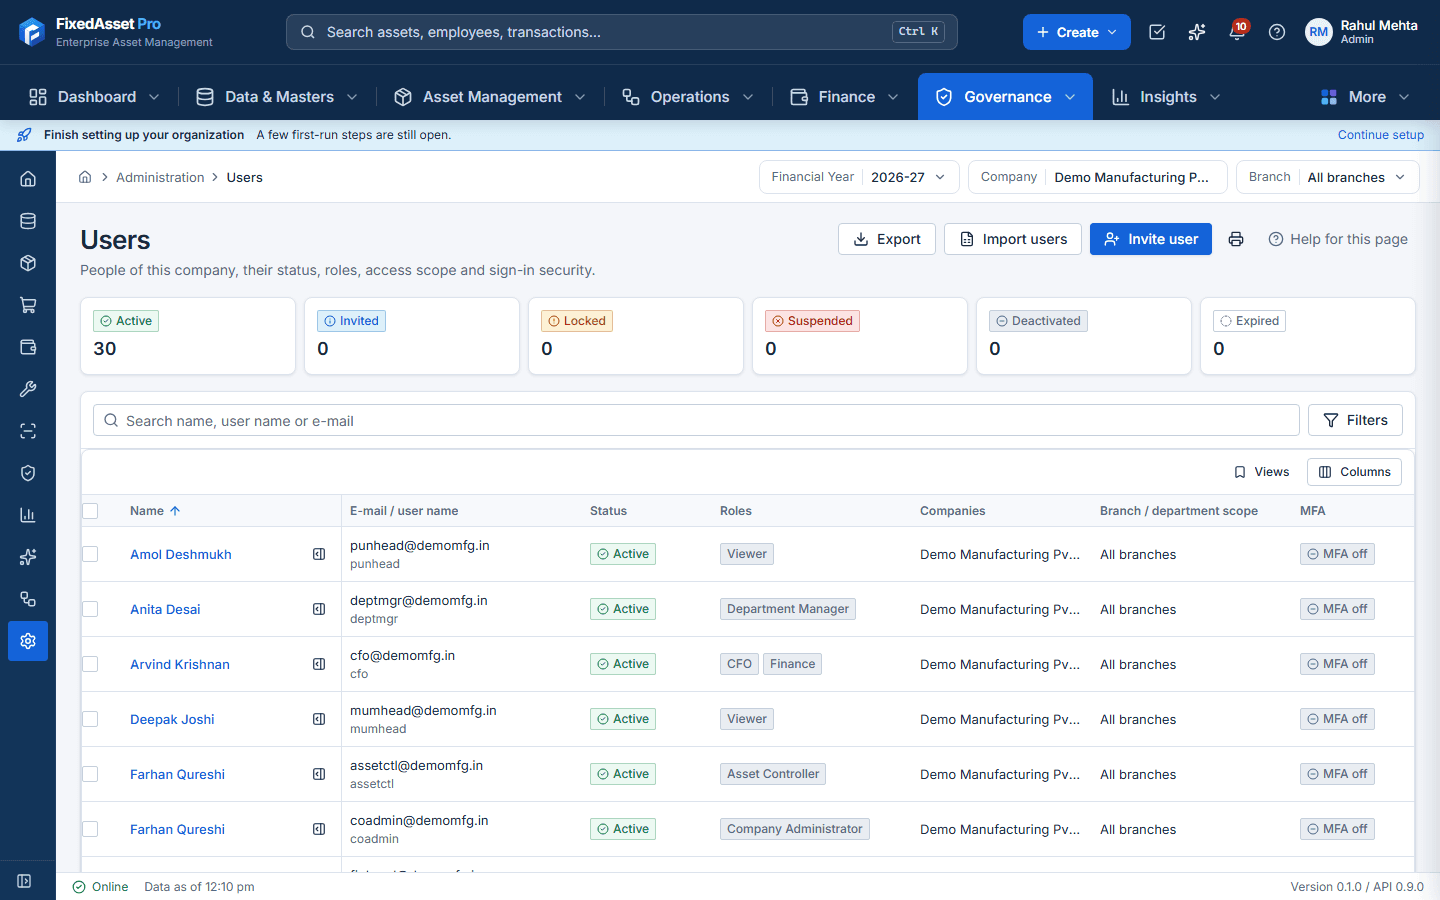
- user account data: usernames, roles, permissions, sign-in and session records, IP addresses, multi-factor authentication settings;
- records linking individuals to assets: custody assignments, handovers and acknowledgements, verification results, maintenance and approval actions;
- audit trail entries identifying who made each change and when;
- photographs and documents uploaded by the Customer, such as invoices, insurance policies, lease agreements and evidence files, which may contain personal data;
- questions entered into the AI assistant and the related answers.
4.6 Special care. The cloud service is designed for business asset records. The Customer should not upload more personal data than is needed for these purposes, and should not upload data of children or financial account credentials of individuals.
5. Customer's instructions and obligations
5.1 The Customer's instructions to the Provider are this DPA, the Terms of Service, and the configuration and use of the cloud service by the Customer's authorised users and administrators. Any additional instruction must be in writing and agreed by the Provider, which may charge for work outside the normal scope of the service.
5.2 The Customer is responsible for:
- having a lawful ground under the DPDP Act for the processing of Customer Personal Data and giving any notices required to Data Principals;
- the accuracy and completeness of Customer Personal Data, and keeping it up to date where it may be used to make decisions affecting a Data Principal;
- configuring user access, roles, retention settings and AI settings appropriately;
- responding to requests from Data Principals, with the Provider's assistance under section 11;
- notifying the Board and Data Principals of a Personal Data Breach where the DPDP Act requires the Data Fiduciary to do so.
6. Provider's obligations
The Provider will:
- process Customer Personal Data only on the documented instructions of the Customer, unless required to do otherwise by law, in which case it will inform the Customer before processing unless the law prohibits this;
- inform the Customer promptly if, in its opinion, an instruction infringes the DPDP Act;
- not sell Customer Personal Data, not use it for its own purposes, and not use it to train language models;
- not combine Customer Personal Data with data of other customers; each organisation's data is logically separated in the service;
- implement and maintain the security measures described in section 8;
- assist the Customer as described in sections 11, 12 and 13.
7. Confidentiality of personnel
7.1 The Provider ensures that its staff and contractors authorised to access Customer Personal Data are bound by written confidentiality obligations or an appropriate statutory duty of confidentiality, and access it only as needed to provide the service.
7.2 Access by the Provider's staff to the Customer's workspace is subject to the support access controls in section 9.
8. Security measures
8.1 Taking into account the nature of the processing and the risks to Data Principals, the Provider implements reasonable security safeguards to prevent Personal Data Breaches, including the following measures, which are built into the cloud service:
- Encryption in transit: connections between users' browsers or the mobile app and the service use HTTPS/TLS.
- Password protection: user passwords are stored only as salted scrypt hashes; verification and one-time codes are stored only as hashes.
- Authentication controls: password policy and account lockout, multi-factor authentication (authenticator app, recovery codes, e-mail one-time code), and optional single sign-on through LDAP / Active Directory or OpenID Connect.
- Access control: role-based permissions with built-in and custom roles, scoped by organisation, company, branch and location; amounts hidden from users without finance rights; logical separation of each organisation's data.
- Session and API controls: sessions can be listed and ended; API keys for integrations are scoped, expire, can be restricted by IP address and are rate-limited.
- Audit logging: every change records who, when, the old and new values and the reason; the audit log is sealed every 15 minutes into a hash chain, verified daily and cannot be switched off. AI activity is recorded in a separate hash-chained log.
- Document integrity: documents are versioned; evidence packs carry a SHA-256 checksum and can be re-checked for integrity.
- Backups: scheduled backups are stored as AES-256-GCM encrypted archives, with verification and restore testing.
- Secrets handling: passwords, codes, keys and other secrets are excluded from logs and are never returned by the service's interfaces.
- Support access controls: as described in section 9.
8.2 The Provider may update these measures over time, provided that the overall level of protection is not reduced.
9. Support access to the Customer's workspace
9.1 The Provider's support staff access the Customer's workspace only to resolve a support request, through a support session that:
- is linked to a support ticket and records the reason;
- is limited in time (at most eight hours) and ends automatically when it expires;
- carries no more permissions than the user being helped, and is read-only by default;
- cannot export or download data in any mode;
- can make changes only if a second, separately authorised member of the Provider's staff approves an elevated session, and even then cannot delete records, post or approve transactions, close periods, change billing, or change users, roles, passwords, MFA, SSO or API keys;
- records every request made during the session, and attributes any change to the support person in the Customer's audit trail.
9.2 The Customer can see support sessions in its own audit trail and can end a session at any time.
10. Sub-processors
10.1 The Customer gives general authorisation to the Provider to engage Sub-processors in the following categories:
- infrastructure and hosting providers (servers, databases, object storage and backup storage);
- e-mail delivery providers for messages sent by the service;
- providers of security services such as malware scanning of uploaded files, where used.
Payment service providers (such as Razorpay or Stripe) receive payment data directly from the Customer on their hosted pages and process subscription payments for the Provider; they do not receive Customer Data.
10.2 The current list of Sub-processors, with their location, is available on request to support@globalsynapsetech.com.
10.3 The Provider will impose on each Sub-processor data protection obligations no less protective than those in this DPA, and remains responsible to the Customer for the Sub-processor's performance.
10.4 The Provider will inform the Customer of any intended addition or replacement of a Sub-processor at least 30 days in advance. The Customer may object on reasonable data protection grounds within that period. The parties will then discuss the objection in good faith; if no solution is found, the Customer may terminate the affected subscription and receive a refund of prepaid Fees for the unused period.
10.5 Customer-selected services. Systems that the Customer itself connects to the service, such as its ERP, its directory or single sign-on provider, or a third-party cloud AI provider enabled by the Customer's administrator, are not Sub-processors of the Provider. Data sent to them is transferred on the Customer's instructions and under the Customer's own agreements with them.
11. AI features
11.1 The AI features of the service read only the data that the requesting user is permitted to see, never change records on their own, and present extracted data as drafts for a user to review.
11.2 By default, AI processing uses built-in rules or a language model operated as part of the service. A third-party cloud AI provider is used only if the Customer's administrator enables it, confirms a warning, supplies the provider's endpoint and key, and selects the features and data classes that may be sent; sending document text requires a second confirmation. Database records are not sent; answers are computed within the service.
11.3 AI activity logs are retained for the period configured by the Customer (365 days by default) and are then purged automatically.
12. Assistance with Data Principal requests
12.1 The service gives the Customer's administrators the means to find, correct, update, export and deactivate personal data of users and other Data Principals, which the Customer can use to respond to requests under the DPDP Act.
12.2 If the Provider receives a request directly from a Data Principal about Customer Personal Data, it will not respond on the merits (except to direct the Data Principal to the Customer) and will forward the request to the Customer without undue delay.
12.3 Where the Customer cannot fulfil a request using the service, the Provider will provide reasonable assistance on request.
13. Personal Data Breach
13.1 The Provider will notify the Customer without undue delay, and in any event within 48 hours, after becoming aware of a Personal Data Breach affecting Customer Personal Data.
13.2 The notification will describe, to the extent then known: the nature and extent of the breach, the categories and approximate number of Data Principals and records concerned, the likely consequences, the measures taken or proposed to mitigate it, and a contact person. Information not available at first will be provided in phases as it becomes available.
13.3 The Provider will take reasonable steps to contain and remedy the breach, will cooperate with the Customer, and will provide the information the Customer reasonably needs to notify the Board and affected Data Principals as required by the DPDP Act. The Provider will not notify Data Principals of the Customer directly unless the Customer asks it to or the law requires it.
13.4 Notification of a breach is not an acknowledgement of fault or liability.
14. Assistance with compliance
The Provider will give the Customer reasonable assistance, taking into account the nature of the processing and the information available to it, with data protection impact assessments, periodic audits and other obligations that apply to the Customer under the DPDP Act, including where the Customer is notified as a Significant Data Fiduciary.
15. Return and deletion at the end of the service
15.1 During the subscription, the Customer can export Customer Data at any time through the reports, exports and document download functions of the service.
15.2 After the subscription ends, Customer Data remains available for export for the period stated in the termination or expiry notice. At the end of that period, the Provider will delete Customer Personal Data from the active systems of the service. Copies in encrypted backups are deleted as those backups expire under the backup retention schedule, and are not restored except to recover the service.
15.3 The Provider may retain Customer Personal Data where required by law, in which case it will keep it confidential and process it only for that purpose. On request, the Provider will confirm deletion in writing.
16. Audits and information
16.1 On written request, the Provider will make available to the Customer the information reasonably necessary to demonstrate compliance with this DPA, such as descriptions of its security measures and answers to security questionnaires.
16.2 If that information is not sufficient, or if required by the Board or a competent authority, the Customer may conduct an audit, by itself or through an independent auditor bound by confidentiality, no more than once a year, on at least 30 days' written notice, during business hours and in a manner that does not disrupt the service or compromise the security or confidentiality of other customers' data. Each party bears its own costs, unless the audit reveals a material breach by the Provider.
16.3 The Provider does not currently claim any third-party security certification. If it obtains one, it will make the relevant report available to the Customer, which may then be used in place of an audit where appropriate.
17. Transfers outside India
17.1 Customer Personal Data may be processed in India or in other countries where the Provider or its Sub-processors operate. The Provider will transfer Customer Personal Data outside India only as permitted by the DPDP Act and not to any country or territory to which the Central Government has restricted transfers.
17.2 Information about the hosting location of the service and its backups is available on request.
17.3 Where other data protection laws apply to the Customer, the parties will agree such additional transfer terms as those laws require.
18. Liability and precedence
18.1 Each party's liability under this DPA is subject to the limitations and exclusions of liability in the Terms of Service.
18.2 If there is a conflict between this DPA and the Terms of Service about the processing of Customer Personal Data, this DPA prevails.
18.3 This DPA remains in force as long as the Provider processes Customer Personal Data. It is governed by the laws of India, and disputes are subject to the jurisdiction set out in the Terms of Service.
19. Contact
Questions about this DPA, notices under it and requests for the Sub-processor list can be sent to:
- E-mail: support@globalsynapsetech.com
- Website: www.globalsynapsetech.com
- Postal address: Global Synapse Technologies, 218-A, 1st Floor, Rama Market, Pitampura, Delhi 110034, India
- Phone: +91-920 575 7755 (Monday to Friday, 9:00 to 18:00 IST)
The Provider's Grievance Officer can be reached at support@globalsynapsetech.com.